

 By rssfeeds-admin

 Google named Exabeam a Google Unified Security Recommended partner. Google launched this program in 2025 with three inaugural members: CrowdStrike, Fortinet and Wiz. Since then, Google has reportedly added Palo Alto Networks, with Exabeam now expected to join the list.
This designation recognizes the strength of combining Exabeam New-Scale Analytics with Google Security Operations.
Google SecOps’ cloud-native security operations platform empowers security teams to better detect, investigate, and respond to cybersecurity threats. Exabeam extends Google SecOps with behavioural intelligence, enabling faster insider threat detection, investigation, and response.
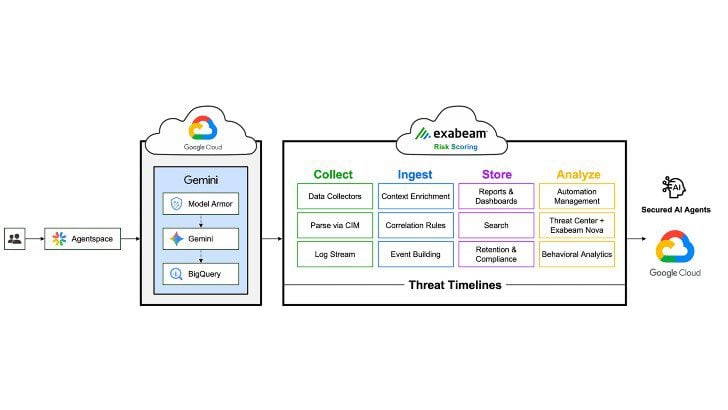
The Exabeam solution connects directly with Google Security Operations data, enabling users to work within a single integrated view. With Exabeam, users identify patterns and react faster to risks that remain hidden when viewing individual events. Using integrated data sharing, analysts apply Exabeam’s behavioural intelligence to a wider dataset. This helps identify actual issues, flag false positives early and saves time on diagnosis.

Pete Harteveld, CEO of Exabeam, commented, “Being named a Google Unified Security Recommended partner reflects the strength of our collaboration with Google Cloud and the value we deliver together for customers.
“Security teams are struggling with alert overload. What they’re missing is insight into the behaviors that represent real risk to their enterprise. Our work with Google Cloud brings this behavioral intelligence directly into Google Security Operations, helping customers identify abnormal activity in the context of behavior across both human users and AI agents.”
Unified Solution
Both platforms run on Google Cloud, allowing security teams to share data without incurring egress charges. This removes the need to move data into a separate analytics environment and reduces operational complexity.
The integration offers several additional benefits:
- Accelerate TDIR workflows: Exabeam validation testing showed organizations accelerating TDIR workflows by up to 80%.
- Detect insider risk earlier: Apply New-Scale Analytics to Google Security Operations data to identify high-risk activity across users, entities, service accounts, and AI agents.
- Reduce analytics complexity: Use integrated data sharing to apply Behaviour Intelligence to data already in Google Security Operations without maintaining a separate analytics environment.
- Available on Google Cloud Marketplace: Procure Exabeam New-Scale Analytics through Google Cloud Marketplace, where eligible purchases can apply toward existing Google Cloud spend commitments.
- Secure both users and agents: Extend coverage to AI agents by analysing Gemini Enterprise Agent Platform and Model Armor activity alongside user behaviour, behavioural analytics, dynamic risk scoring, and agent-powered TDIR workflows to detect risky human and non-human identity activity.
Securing AI agents is more important than ever
AI agents can now work across apps, tools, data and business processes. That makes them useful, but it also makes them harder to monitor. Google describes Google Unified Security as an AI-infused approach. It uses Gemini and threat intelligence to support security workflows at scale.
While individual agent actions often resemble human behaviour and appear low-risk, significant concerns remain. Chen et al, in How Your Credentials Are Leaked by LLM Agent Skills: An Empirical Study (June 2026), found several examples.
The study identified a cumulative risk: 73.5% of vulnerabilities stemmed from debug logging. Individually, a log statement is benign. However, when an agent executes 100+ tool invocations, and each logs a token, the cumulative exposure becomes a data exfiltration channel.
It also identified that 89.6% of the affected agent skills were exploitable during routine execution without elevated privileges. Thus, proving that “normal” behaviour can still leak credentials when viewed as a sequence.
Addressing the Agentic Challenge
Exabeam states its New-Scale Analytics adds behavioural analytics, dynamic risk scoring, and AI-powered investigations to Google Security Operations. The Exabeam solution integrates with Gemini Enterprise Agent Platform and Model Armor to mitigate this risk.
- Gemini Enterprise Agent Platform helps organisations build, manage and govern enterprise AI agents. In this context, it provides activity signals that can be reviewed alongside other security data.
- Model Armor gives teams more information about large language model activity, including prompts and responses, so that this activity can be assessed as part of security monitoring.
Those signals can help security teams see how agents behave, which systems they use and where unusual activity may appear. Exabeam analyses this activity in New-Scale Fusion alongside user behaviour. It designed its New-Scale Analytics product to learn normal activity, apply risk scores, and highlight activity that needs investigation.
Exabeam also says its Nova cybersecurity agents can support threat detection, investigation and response workflows by adding behavioural context and helping analysts prioritise work.
Dr. Andre Alfred, Sr. Director, Cloud Security Threat Operations, Google Cloud, stated, “As organizations shift toward AI-driven security, operations and autonomous agents, open interoperability across the technology stack is vital.
“The Google Unified Security Recommended program creates deep technical collaboration with market-leading security vendors to minimize integration overhead, enabling security teams to focus on outcomes rather than complexity. We’re excited to welcome Exabeam to the Google Unified Security Recommended program to help customers strengthen their defenses with unified, AI-driven protection.”
Enterprise Times: What does this mean
Using Exabeam’s new scale analytics, security teams can better leverage its behavioural intelligence to spot anomalous patterns from both humans and agents. With agents now capable of performing many more tasks than humans, it is critical that organisations have the ability to track, monitor and analyse events faster than ever before.
Using Exabeam and Google SecOps, teams can benchmark normal behaviour and better detect and identify anomalies. No matter how small, that signal compromised accounts, malicious insiders, or risky AI agent behaviour. Security teams can now better identify evolving trends and patterns through the platform. They can react faster and mitigate risks as they emerge.
Google Security Operations customers can access Exabeam New-Scale Analytics through Google Cloud Marketplace, where eligible purchases count toward existing Google Cloud spend commitments.
Read More…
The post Google Backs Exabeam for Unified Security appeared first on Enterprise Times.
Discover more from RSS Feeds Cloud
Subscribe to get the latest posts sent to your email.